Outlook Will Block MSIX Installer Attachments in November: A Timeline of Microsoft’s Attachment Crackdown
Starting in November, Outlook on the web and the new Outlook for Windows will block .msix and .msixbundle attachments by default. Here is how the change fits Microsoft’s broader crackdown, and how layered defenses help.
Here Is How Layered Defenses Help
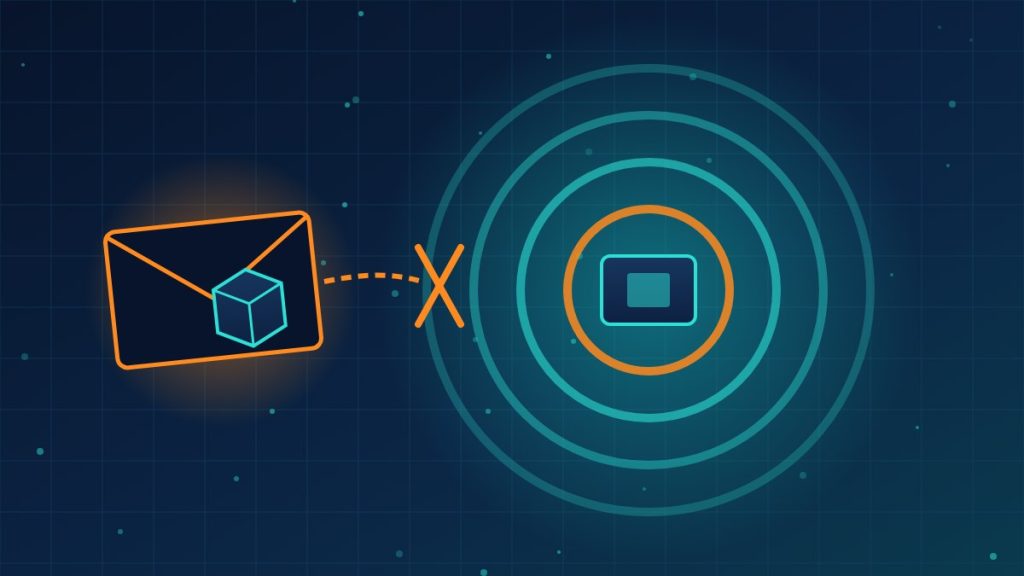
Attackers love anything that lets them slip software onto a computer through an email. Microsoft is closing one more of those doors next month. Starting in November, .msix and .msixbundle files will join the list of attachments Outlook blocks by default. MSIX is a modern Windows app installation package, and a bundle groups several of those packages into a single file so it works across different hardware types.
How we got here: a timeline
- Since at least June 2022: Attackers abuse .library-ms and .search-ms files in phishing and malware campaigns, including attacks on government organizations.
- June 2025: Outlook begins blocking .library-ms and .search-ms attachments.
- October 2025: Microsoft announces that Outlook on the web and the new Outlook for Windows will stop displaying risky inline SVG images, which were also being used in attacks.
- October 2026: A Microsoft 365 message center update announces that .msix and .msixbundle will be added to the BlockedFileTypes list in the default OWA mailbox policy and in any custom policies in each tenant.
- Early November 2026: The rollout begins for Exchange Online customers.
- Mid-November 2026: General availability is expected. From then on, users of Outlook on the web and the new Outlook for Windows can’t send, receive, open or download these attachments.
Do admins need to do anything?
Usually not. Microsoft says most organizations won’t notice because these file types are rarely used. If your business does send MSIX packages by email, administrators can allow them again by adding the extensions to the AllowedFileTypes property of the relevant OwaMailboxPolicy. The report covers Outlook on the web and the new Outlook for Windows; it doesn’t say anything about the classic Outlook desktop app, so confirm with Microsoft’s documentation if you still run it.
Sergiu Gatlan reported the change for BleepingComputer, including links to Microsoft’s full list of blocked attachment types.
Why a single block isn’t enough
Blocking a file type in email is a useful step, but attackers adapt. They can switch to a different file type, hide an installer inside an archive, or send a download link instead of an attachment. Layers make sure that when one control is bypassed, another is still in place. Any products named below are examples only. Comparable tools exist from many vendors, and the right mix depends on your environment.
Layer 1: Filter at the mail gateway
Use your mail platform’s attachment policies, or a separate email security service, to block risky file types and scan links and archives, not just what Outlook happens to block by default.
Layer 2: Control what can be installed
Application control, such as Microsoft’s built-in App Control for Business and AppLocker or a comparable third-party tool, can stop unapproved installers from running even if one gets through by another route.
Layer 3: Remove everyday admin rights
Staff who don’t log in as local administrators can’t casually install software. That one change limits a large share of malware attacks.
Layer 4: Watch the endpoint
Endpoint detection and response tools can catch suspicious behavior after a file is opened and isolate a device before an infection spreads.
Layer 5: Give people a clear rule
Tell staff plainly that software never arrives by email at your company, and give them a quick way to report messages that try.
What this means for your company
- Check before mid-November. Ask whether any team or software vendor sends you MSIX packages by email. If so, plan another delivery method or a deliberate exception.
- Review your own blocked list. Microsoft’s defaults are a floor, not a ceiling. Consider blocking other installer and script file types your business never needs to receive.
- Deliver software through managed channels. Pushing apps through your device management or a company portal removes any legitimate reason for installers to show up in email.
Need help tightening email attachment policies and application control across Microsoft 365? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author