A Poem on GitHub Is Steering a Botnet of Hijacked AI Servers: PoeLLM in Questions and Answers
Researchers say PoeLLM malware has compromised more than 3,400 servers, many running exposed AI tools, and finds its control servers by decoding words hidden in a poem on GitHub.
Companies experimenting with AI often spin up model servers fast and worry about security later. A new cryptomining campaign is taking advantage of exactly that habit, and it hides its instructions in an unlikely place: a poem.
What is PoeLLM?
It is botnet malware tracked by Lumen’s Black Lotus Labs. On infected machines it shows up as an ELF file named libgcrypt. Once installed, it can open a remote shell, run the XMRig and Iron cryptocurrency miners, scan for other web services and deploy exploits.
How big is it?
The researchers count more than 3,400 compromised servers, with as many as 800 infected systems active on its busiest single day. The campaign has been running since at least April, has grown considerably since, and has used at least 11 command-and-control (C2) servers so far. Victims are mainly in the United States and Western Europe.
Why does a poem matter?
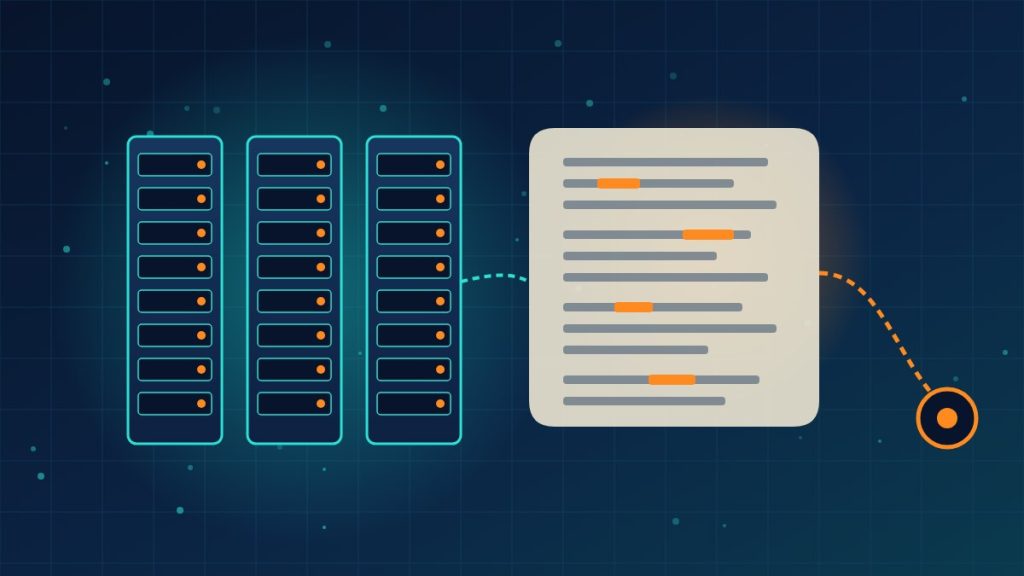
Instead of hard-coding where to call home, the malware reads a poem titled “On the Nature of Connection” from a file called dash.css in a GitHub repository that looks like a fork of Node.js. It pulls out four words or phrases, converts them to numbers using a built-in dictionary and assembles an IPv4 address for its C2 server. To move the botnet to a new server, the operator just edits the poem. That has happened 11 times so far, and the researchers think there may be at least one more change.
Which systems are being hit?
Many victims were running internet-exposed AI tools such as LiteLLM and Ollama, the Gotenberg PDF converter or the Gitea development toolkit. The researchers also found signs of targeting against Ivanti Sentry. Black Lotus Labs notes that AI deployments are attractive because they are often poorly configured, left open to the internet and backed by powerful GPUs that are ideal for mining.
How does it spread?
Each compromised server becomes a launchpad. It scans ports 3000 and 4000, which are associated with Gotenberg and LiteLLM, and tries to exploit CVE-2026-42271, a flaw in LiteLLM’s MCP server test endpoints. That bug was first disclosed as needing authentication, but Horizon.ai researchers confirmed it can be chained with CVE-2026-48710 for remote code execution without logging in.
Who is behind it?
There is no firm attribution. Based on comments in the code and an administrative server hosted in Italy, the researchers assess with moderate confidence that the operator is Italian. Several of the C2 servers had vulnerable router admin pages, which suggests the attacker reused hijacked routers. Infected machines connect to a Russian mining service called Kryptex.
What do the researchers recommend?
Install the latest security updates, cut down on public internet exposure for important systems, allow outside access only from trusted IP addresses, and check network logs for connections to the indicators of compromise Black Lotus Labs has published.
Bill Toulas walked through the research for BleepingComputer, including a correction raising the compromised-server count to 3,400.
What this means for your company
If anyone in your organization has set up an AI model server, an LLM gateway or a self-hosted developer tool, find out where it lives and who can reach it. These services are often launched as quick experiments and then forgotten, without passwords, patching or monitoring. Put them behind a VPN or an IP allow list, keep them updated, and watch for unexplained spikes in CPU or GPU usage, which can be the first sign that someone else is using your hardware to make money.
Need help finding and locking down exposed AI and developer tools on your network? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author