Attackers Are Now Hijacking Exposed Node-RED Automation Servers With a Single Web Request
A maximum-severity flaw tied to Node-RED, the browser-based automation tool found in industrial gateways and many in-house projects, is being exploited to plant Linux bots and hidden command backdoors. Here is the timeline and a short triage list.
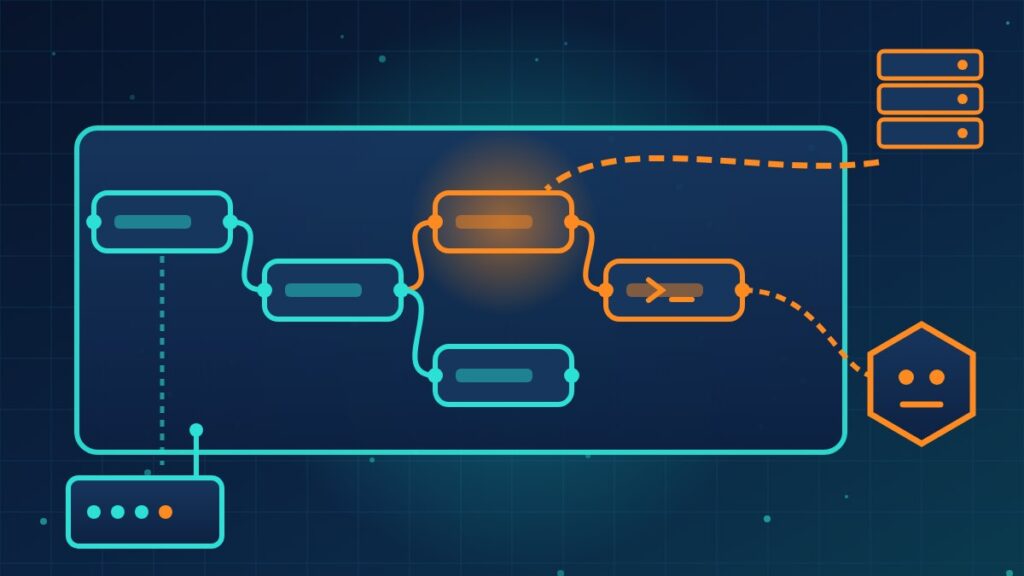
Node-RED is the kind of tool that quietly ends up everywhere. It lets people wire together sensors, web services and scripts by dragging boxes around a browser page, and it ships inside industrial gateways as well as in countless small automation projects. As of this week, attackers are actively scanning for copies of it that do not ask for a password and taking them over automatically.
The details here come from SecurityWeek’s report on the attacks, with technical specifics from The Hacker News. Both draw on findings published by the vulnerability intelligence firm VulnCheck.
How it unfolded
- August 11: Siemens discloses CVE-2026-58115, rated 10 out of 10, after finding that its SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed expose the Node-RED web interface without authentication. Anyone who can reach it can build a malicious flow and run code on the device with the highest privileges. Version 4.3.4.1 and later contain the fix.
- October 30: VulnCheck’s honeypots record the first successful attack. A single request deploys a flow, starts it automatically and downloads a Linux bot from an attacker server, hidden behind three layers of encoding. The traffic came from an IP address on Microsoft’s network (AS8075).
- By November 1: fifteen more attacks arrive from the same address. Some fetch additional payloads disguised with harmless-looking names. Others skip the download entirely and leave a web endpoint wired to a command-execution node, so the attacker can return later and run any command through a URL parameter. That kind of backdoor survives a reboot.
- This week: VulnCheck publishes its findings, warning that scanning for Node-RED instances without its adminAuth protection is now automated.
Is this you?
The CVE itself is listed against the Siemens gateway, but VulnCheck’s warning is broader: if you run Node-RED anywhere and its editor is reachable without a login, you should assume it is being probed. That includes a building-automation box a contractor installed, a monitoring dashboard someone in operations built, or a test server a developer forgot to turn off.
Triage in five steps
- Ask your IT provider, operations staff and any automation contractors whether Node-RED runs anywhere in your environment, including inside vendor appliances.
- Check whether its editor or HTTP endpoints can be reached from the internet. If they can, block that access at the firewall today.
- Turn on authentication for the editor and admin API (Node-RED supports password and single sign-on options) and protect HTTP nodes and dashboards with credentials. Siemens also suggests removing Node-RED entirely where it is not needed.
- If you own SIMATIC IoT2050 Advanced devices, move them to version 4.3.4.1 or later.
- Review deployed flows for anything you did not build, especially new HTTP endpoints or nodes that run system commands. If you find one, treat the device as compromised and get incident response help before simply deleting it.
What this means for your company
Low-code and automation tools are built for convenience, and convenience often means the default setup trusts whoever connects. Those tools tend to sit outside the normal patching and inventory routine because nobody thinks of them as servers. Any device or tool that can run commands deserves the same three basics as your main systems: you know it exists, it requires a login, and it is not reachable from the open internet unless there is a clear reason.
Not sure what automation tools or smart gateways are running on your network, or who can reach them? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author