Fake AI Ad Tools Are Phishing Marketing Teams: How the ‘Connect’ Trap Works, Step by Step
A phishing operation dressed up as ad products for ChatGPT, Gemini, Claude and other AI brands is stealing ad account logins and MFA codes with fake browser windows. Here is how it works.
Marketing teams are being targeted by a phishing campaign that borrows the names of popular AI brands. Researchers at browser security company Island found fake advertising tools themed around ChatGPT, Gemini, Claude and Perplexity, all designed to capture login details and multifactor codes. The bait leaned on the recent launch of Meta’s Muse AI agent. Here is how the scheme plays out.
The attack in six steps
- Pick valuable targets. The pages go after agency staff, media buyers and administrators whose ad accounts reach multiple downstream clients. Those accounts can be drained through fraudulent ad campaigns or resold to other criminals for significant sums.
- Offer a tempting tool. The fake AI products promise help reaching buyers, getting ad briefs, and planning and auditing campaigns and spending.
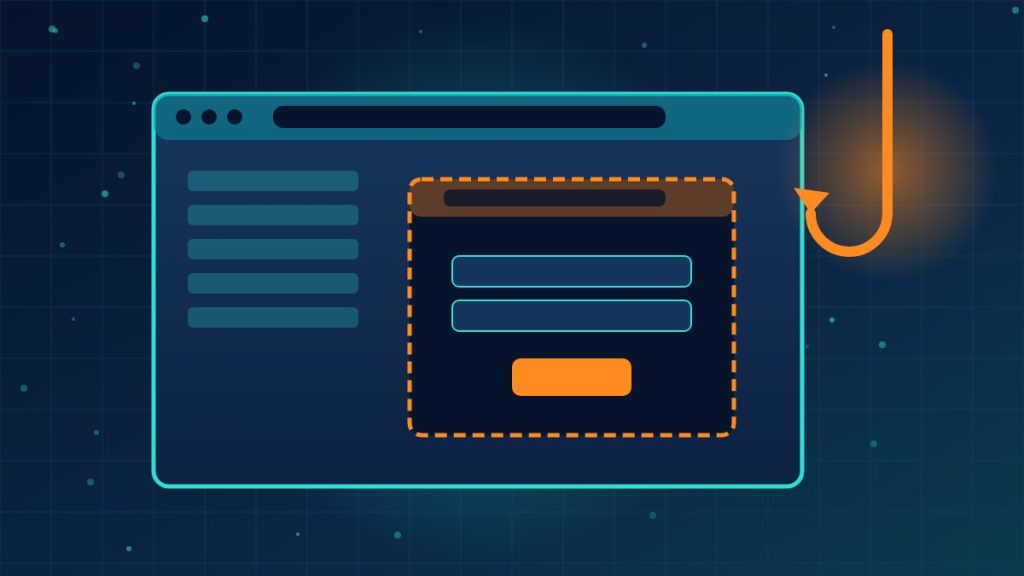
- Ask the victim to connect. To use the tool, the visitor must link their account. Clicking “Connect” opens what looks like a Google sign-in window, complete with an address bar showing accounts.google.com.
- Show a window that isn’t real. That pop-up is a browser-in-the-browser fake: an iframe drawn inside the page to look like a separate window. The technique was devised by researcher mr.d0x in March 2022. The kit adjusts its look for Windows, macOS, iOS and Android, including browser styling and dark mode.
- Hand control to a live operator. Once the victim is in the fake window, a person steers what happens next. They can ask for the password up to three times, request an SMS or authenticator code, show Okta push requests or Google approval prompts, or display a QR code. They can also reject codes, park the victim on a waiting screen, or end the flow whenever they choose.
- Collect and disguise. The platform supports Google, Meta, TikTok and Okta sign-ins. It rebuilds the provider’s interface itself and gathers credentials and MFA state through its own APIs, so the traffic looks like an AI product talking to an unrelated backend.
A bigger operation behind it
Island linked the ad lures to a wider operation that also used fake recruitment offers and refund pages. The pages share a Next.js and Socket.IO stack and common API endpoints, and many run on Vercel frontends with Railway or Render backends. Older source code left in misconfigured public GitHub repositories let researchers trace the activity back to March. The Telegram channel used to control the attacks had received hundreds of victim submissions, though that does not necessarily equal the number of accounts actually compromised.
The tell
A genuine sign-in pop-up is a real browser window: you can drag it outside the browser or resize it. A browser-in-the-browser fake is stuck inside the page and can’t do either.
Bill Toulas covered Island’s findings for BleepingComputer; the researchers’ report lists the URLs tied to the campaign.
What this means for your company
- Ad and social accounts hold real money. Give marketing logins the same protection as finance systems, including the strongest MFA available.
- Prefer phishing-resistant sign-in. Codes and push approvals can be relayed by a live operator. Passkeys and hardware security keys are much harder to phish.
- Teach the drag test. Show staff that a real login window can be moved outside the browser. It takes five seconds and defeats this trick.
- Vet new tools before connecting accounts. Require a quick review before anyone links company accounts to an unfamiliar AI or marketing product.
Need help protecting your marketing and advertising accounts from phishing? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author