Meet VOLTA, the Infostealer That Hands Your Stolen Data to an AI and Asks What You’re Worth
Cisco Talos has documented a Windows infostealer that sends each victim’s stolen data to commercial AI models, which write a ranked dossier of what can be monetized. Here is how it works, step by step, and why it matters for ordinary businesses.
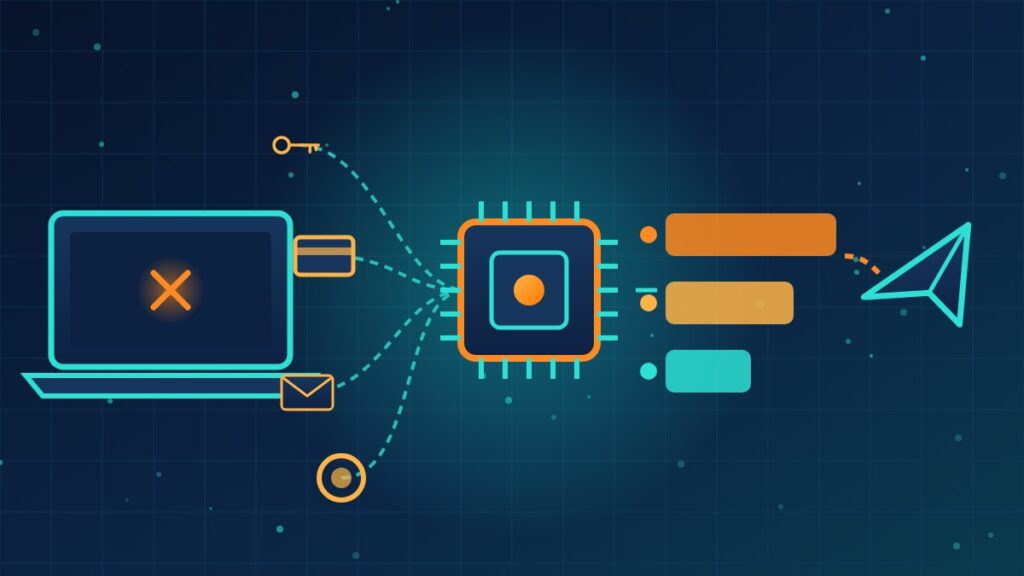
Infostealers have long been a volume business: grab every password and cookie from thousands of machines, then sort through the pile later. A new strain called VOLTA-AUTODOXER, or VOLTA, hands the sorting job to artificial intelligence. Cisco Talos researchers say it bundles up everything it learns about a victim and asks a large language model to rank what that person is worth.
The walkthrough below is based on The Hacker News’ report on the Talos research.
How one infection plays out
- Harvest. On a Windows PC, VOLTA collects what most stealers do: saved passwords and cookies from Chromium-based browsers, Outlook profile data, Slack workspaces, payment cards, crypto wallet seed phrases, gaming and chat sessions, Microsoft OAuth tokens, SSH and cloud keys, Wi-Fi profiles and screenshots.
- First upload. Right away, that raw haul goes to the operator over Telegram.
- Build a profile. The malware assembles what Talos calls an evidence bundle about the person: approximate location and home address, employer and company domain, an inferred birth year, the last four digits of cards, document authorship details and more.
- Ask the AI. The bundle is sent through OpenRouter, a service that routes requests to many AI models. VOLTA tries Anthropic’s Claude Opus 4.6 first, then falls back to Moonshot AI’s Kimi K2 and Google’s Gemini 2.5 Flash if a model refuses. A system prompt casts the model as a “forensic intelligence analyst” and requires a section ranking the victim’s valuables as low, medium or high, plus an assessment of their security habits and password hygiene.
- Second upload. The AI’s write-up travels to Telegram alongside the stolen data.
- Confirm and enrich. Using the stolen session, VOLTA searches the victim’s Gmail for receipts from retailers and delivery services to confirm the home address, then sends those findings in a third upload.
Talos also found a build template with six slots, including the Telegram channel and API keys, filled in for each compiled copy. That suggests VOLTA is either sold as a builder kit or compiled to order, which would put the AI dossier feature in the hands of buyers with little skill of their own. Talos describes the point of the AI layer as taking analytical work off the operator, rather than making attacks faster.
A related trick: making the victim pay for the AI
Talos separately documented a remote access tool called NIK C2 that also sends stolen data to an AI model during an intrusion. If the attacker has not supplied an OpenAI API key, it looks for one in the victim’s environment variables and uses that instead, so the victim’s own account pays for the analysis. That practice, called LLMjacking, also helps hide who is really making the requests.
What this means for your company
The novelty here is not a new way in. VOLTA still depends on someone running a malicious file, and it steals the same things stealers always have. What changes is how quickly a criminal can decide that the bookkeeper’s laptop, with its saved banking session and company email, is the one worth working. The defenses are familiar and worth tightening: keep users from installing unvetted software, use endpoint protection that watches for credential theft, discourage saving passwords in browsers in favor of a managed password manager, require phishing-resistant multifactor sign-in, and treat API keys like passwords rather than leaving them in plain environment variables.
Wondering what an infostealer would find on your team’s laptops today? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author