Synology Issues a Rare Ransomware Warning: Outdated NAS Boxes Are Being Encrypted by C3RB3R
Synology says attackers are exploiting a flaw it patched in December 2024 to encrypt data on NAS devices still running old DiskStation Manager software. Here is how to tell if a box is exposed and what to do before the end of the day.
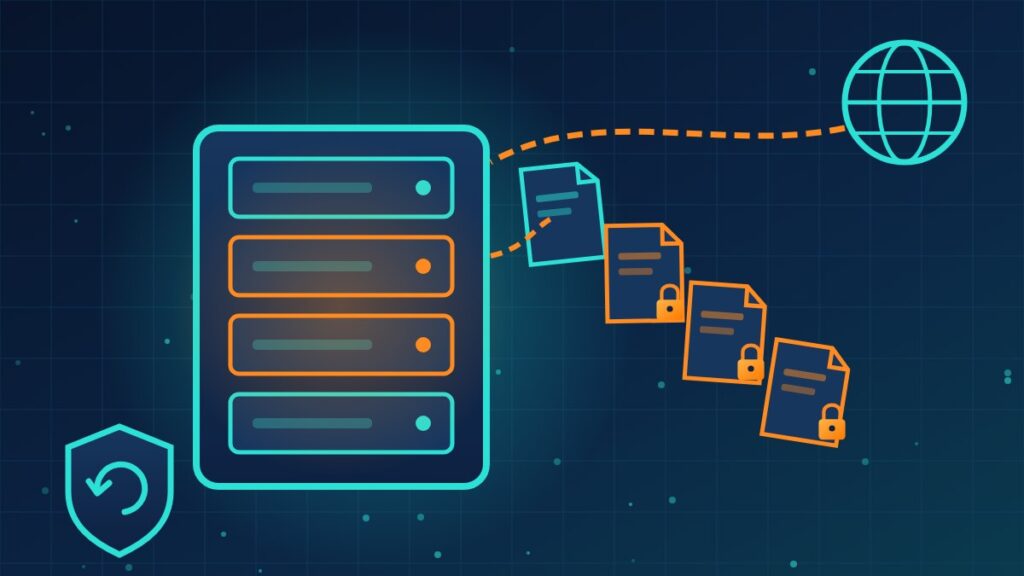
Synology does not often sound the alarm. The storage maker’s last public warning about active attacks on customer devices came in August 2019. Late last week it issued another one: criminals are breaking into Synology network-attached storage (NAS) units that have not been updated and encrypting the files on them with C3RB3R ransomware.
The specifics below are drawn from BleepingComputer’s coverage of Synology’s advisory.
The alert at a glance
- Who is affected: Synology NAS devices running outdated versions of DiskStation Manager (DSM), the operating system on the box.
- How attackers get in: a vulnerability Synology patched in December 2024. The company has not said which one, but its advisory points to a November 2024 bulletin covering flaws that allow code execution (CVE-2024-10441), reading files (CVE-2024-50629) and writing files (CVE-2024-10445) on unpatched units.
- What happens: data is encrypted and the owner is pressured to pay.
- Synology’s instruction: update DSM immediately and turn on automatic updates.
- Extra precaution: block internet access to the device’s web management interface.
- Scale of the target pool: the Shadowserver Foundation tracks more than 380,000 Synology NAS devices reachable from the internet, though it does not say how many are already patched.
How you would know you have been hit
Victims began posting about the attacks more than two weeks ago. They describe encrypted files carrying a .L0CK3D extension and a ransom note named read-me3.txt. The note steers them to a dark web page selling a “C3rb3r Decryptor” for thousands of dollars and warns against trying third-party recovery tools.
C3RB3R is not new. It borrows its name from the Cerber ransomware operation that appeared in 2016, and since December 2021 it has been used against Atlassian Confluence and GitLab servers through known remote code execution and authentication bypass flaws. The common thread is unpatched equipment facing the internet.
Do this now
- Find every Synology unit your company owns, including the one in a branch office or under someone’s desk, and note its DSM version.
- Update DSM to the latest release Synology offers for that model, then enable automatic updates.
- Close any router or firewall rule that exposes the DSM web interface to the internet. If people need remote access, put it behind a VPN or a similar gateway.
- Confirm that the files on the NAS are also backed up somewhere the NAS cannot write to or delete, such as an offline copy or an immutable cloud backup.
- If a unit already shows .L0CK3D files or a read-me3.txt note, disconnect it from the network, preserve what you can, and get incident response help before anyone pays or wipes it.
What this means for your company
A NAS is often the most trusted box in a small office: it holds the shared drive, the scanned documents and sometimes the backups themselves. That makes it a single point of failure when it slips off the patch schedule. A storage device should be patched and inventoried like a server, its admin page should never face the open internet, and at least one copy of your data should live beyond its reach. Those three habits turn a ransomware note into an inconvenience instead of a crisis.
Not sure how many storage devices are on your network, or whether your backups would survive if one were encrypted? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author