One Click on a Shared ChatGPT Link Was Enough to Read Someone’s Private Chats. OpenAI Has Fixed It. Here Is How the Trick Worked
Researchers at Parameter showed that a booby-trapped ChatGPT share link could run their code inside a signed-in victim’s session and read private conversations. OpenAI rated it its most serious category and fixed it in eight days. Here is the chain, step by step, and what it teaches.
Shared ChatGPT conversations get passed around all the time: in email, in team chats, in support tickets and on social media. Security firm Parameter found that one of those ordinary-looking links could be turned into a trap. Opening it, and in the most reliable version clicking a single Preview button, let the researchers’ code act inside the victim’s logged-in ChatGPT account.
This explainer is drawn from The Hacker News’ write-up of Parameter’s research.
The chain, one step at a time
- A normal-looking share link. The attacker builds a ChatGPT conversation and shares it with its public link. The victim does not need to install anything, join a workspace or sign in through the attacker.
- A preview in a locked box. ChatGPT can turn HTML in a chat into a small web page through its Preview feature. Because that page could contain anything, ChatGPT runs it in a sandboxed frame on a separate web address. That sandbox held up.
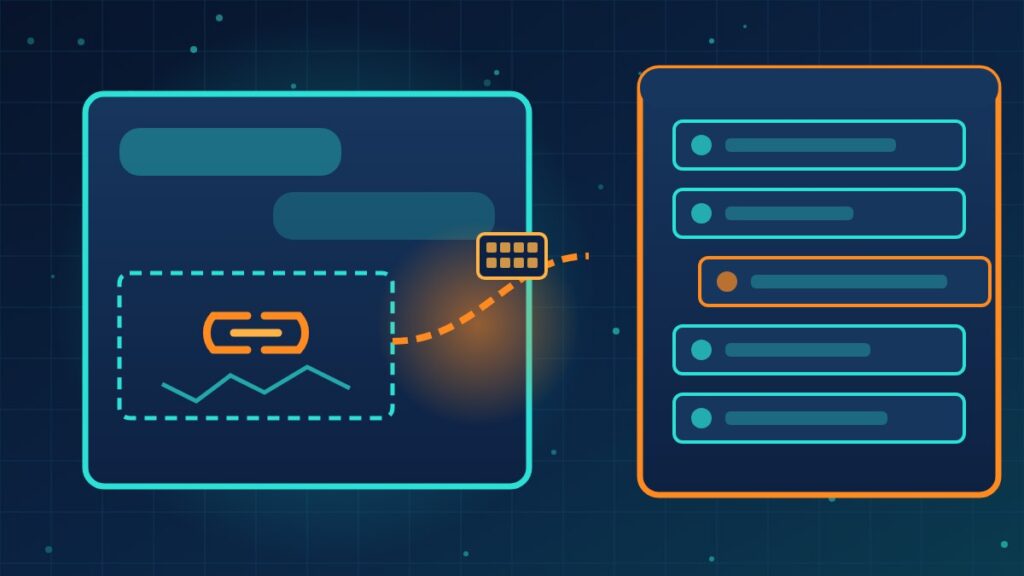
- A second feature opens a side door. The same conversation contained an interactive graph. Drawing it loaded a math library called MathLive into the main ChatGPT page, and MathLive left a listener running that accepted messages about its on-screen keyboard.
- The listener did not check who was talking. Messages between browser frames are only safe if the receiver verifies the sender. This listener accepted keyboard messages from any frame, and those messages could carry raw HTML, so the sandboxed preview could hand attacker-written HTML to the trusted main page.
- A frame the browser trusted. That HTML built a new frame that the browser treated as part of chatgpt.com. ChatGPT’s content security policy blocked inline code but allowed scripts from YouTube, so the researchers used a script loaded from YouTube to supply the code that ran inside it.
- Acting as the victim. From there the code called ChatGPT’s own signed-in interfaces. In the test, it listed recent conversations, opened a private chat that had never been shared and sent a small piece of it to a server the researchers controlled. In their words, they could do essentially anything on behalf of the victim’s account.
In a later version, Parameter made the page open Preview by itself, so simply opening the link was enough.
What was and was not at risk
- This was a controlled test. Parameter ran its private-chat proof between separate accounts it set up, not against real users, and does not report any real-world use of the flaw.
- Parameter reported the bug through OpenAI’s bug bounty program on October 18. OpenAI reproduced it, raised it from P2 to P1, its most serious rating, and by October 26 had rolled a fix across two versions of the ChatGPT web frontend. OpenAI paid $5,000 for the report.
- Users do not need to do anything. The fix was made on OpenAI’s side.
Why it matters beyond ChatGPT
The researchers traced the bug to three design choices lining up: a component that acted on messages without checking the sender, messages allowed to carry raw HTML, and HTML able to create an unsandboxed frame with the site’s identity. The YouTube step was only the final workaround. For anyone building or buying web software, that is the lesson: a strong sandbox can be undone by a small helper library elsewhere on the page.
What this means for your company
AI chat tools now hold a surprising amount of business information, from draft contracts to customer details pasted in for summaries. Treat links into those tools with the same caution as any other link from an unknown sender, keep a clear policy on what staff may paste into AI assistants, and prefer business plans that give you administrative controls and audit logs. When a provider fixes a flaw like this one quickly and openly, that is a point in its favor when you choose which tools to approve.
Wondering what your team is putting into AI tools, and how to set sensible rules around it? Reach out to Layer 7 Data Solutions to discuss how we’ve helped companies similar to yours.
About The Author